CodeRabbit Pledges $1M in Free Deep Scans for Open Source Maintainers
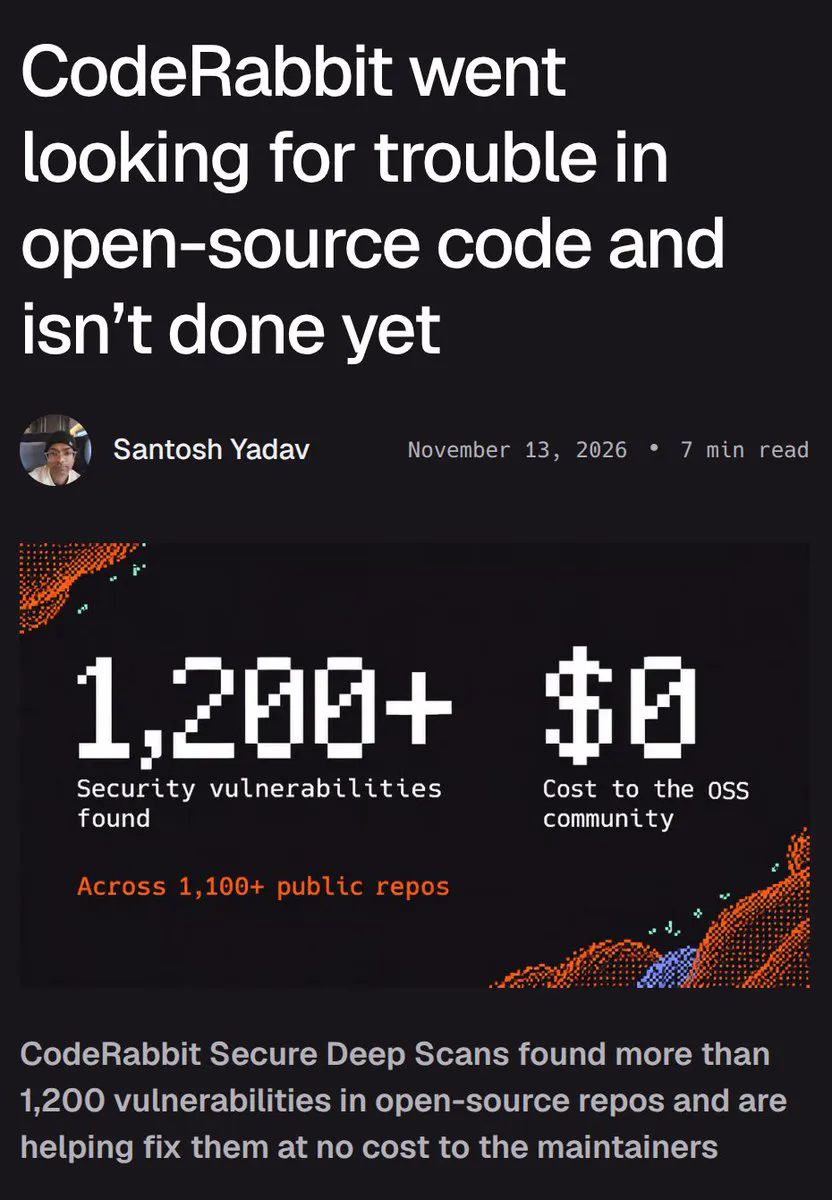
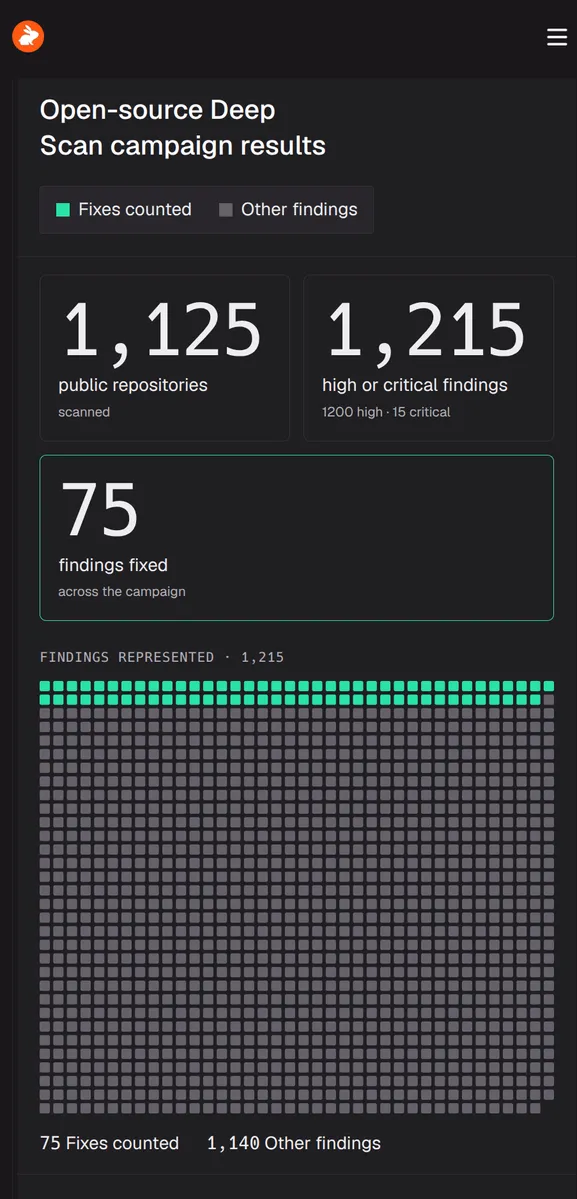
CodeRabbit has pledged $1M to provide free Deep Scans to open source maintainers. The service has already scanned 1,125 public repositories, surfacing 1,215 high or critical findings with 75 already fixed. Deep Scan maps entry points, trust boundaries and access checks, then traces attacker paths like a penetration tester across the codebase.
Related Entities
Full Report
Rohan Paul (@rohanpaul_ai) · 2026-11-13 19
Exploit agents work 24/7, open source maintainers work after hours. that problem need to be solved.
@coderabbitai put $1M into free Deep Scans for open-source maintainers: 1,215 high or critical findings across 1,125 public repos, 75 already fixed, at no cost to the projects.
@coderabbitai's Deep Scan first maps every entry point, trust boundary and access check in a repo, then walks the paths an attacker would take, like a penetration tester covering the whole codebase.
↳ 引用 @coderabbitai (CodeRabbit): Attackers have AI agents probing open-source code 24/7 & we think maintainers should too!
CodeRabbit ran Deep Scans on 1,125 public repos with 1,215 high or critical findings, 75 of which are already fixed.
Your first Deep Scan is on us, up to $1K for orgs with 2+ people.