CodeRabbit 投入 100 万美元为开源维护者免费提供深度扫描
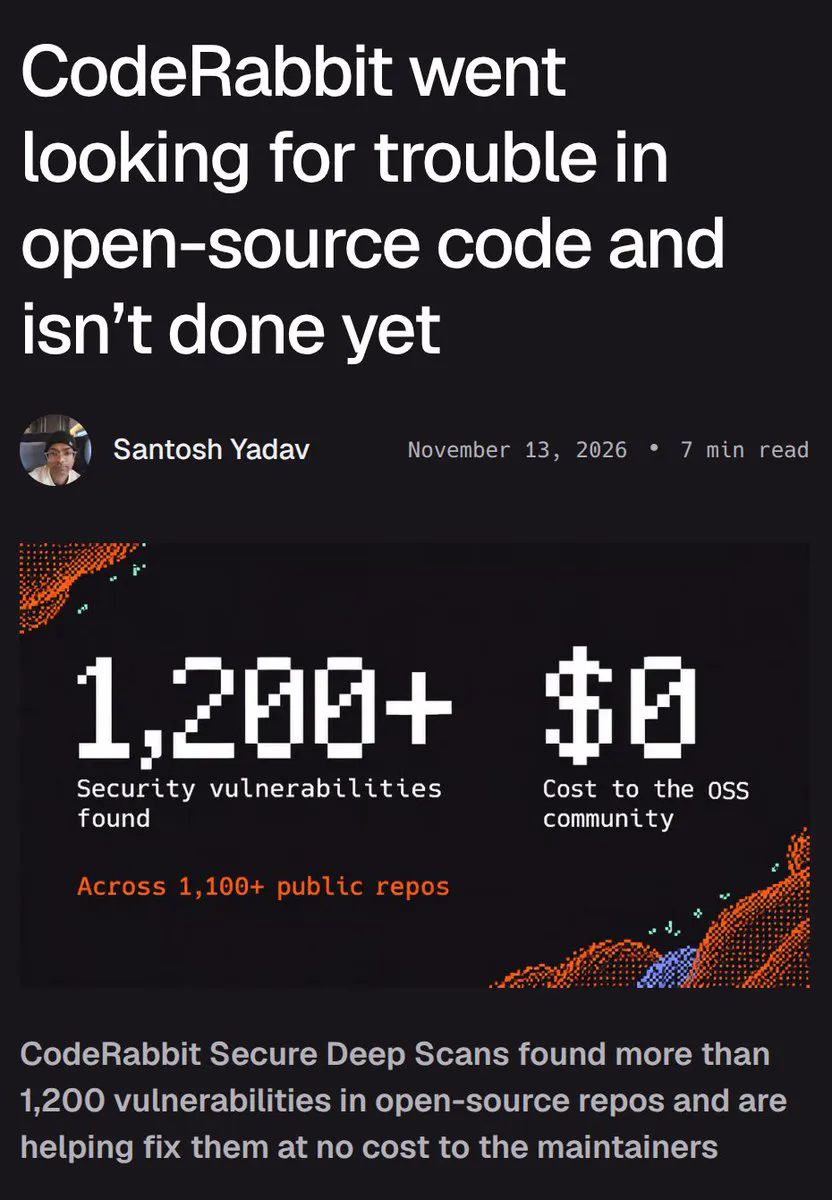
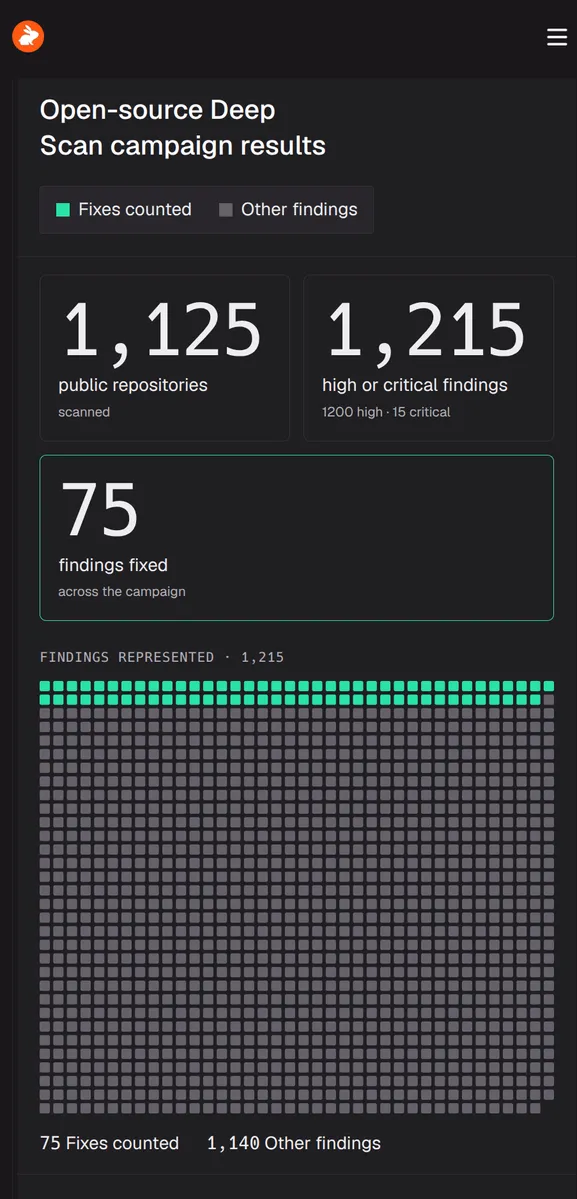
CodeRabbit 宣布投入 100 万美元,为开源维护者免费提供 Deep Scan 安全扫描服务。该服务已覆盖 1,125 个公开仓库,发现 1,215 个高危或严重问题,其中 75 个已完成修复。Deep Scan 会先梳理仓库的入口点、信任边界与访问控制,再模拟攻击者路径进行全代码库渗透式排查。
报道正文
Rohan Paul (@rohanpaul_ai) · 2026-11-13 19
Exploit agents work 24/7, open source maintainers work after hours. that problem need to be solved.
@coderabbitai put $1M into free Deep Scans for open-source maintainers: 1,215 high or critical findings across 1,125 public repos, 75 already fixed, at no cost to the projects.
@coderabbitai's Deep Scan first maps every entry point, trust boundary and access check in a repo, then walks the paths an attacker would take, like a penetration tester covering the whole codebase.
↳ 引用 @coderabbitai (CodeRabbit): Attackers have AI agents probing open-source code 24/7 & we think maintainers should too!
CodeRabbit ran Deep Scans on 1,125 public repos with 1,215 high or critical findings, 75 of which are already fixed.
Your first Deep Scan is on us, up to $1K for orgs with 2+ people.