Anthropic 推出企业前沿安全护栏 EFS
Anthropic 宣布推出“企业前沿安全护栏”(EFS),旨在结合零数据保留(ZDR)隐私保护与先进的滥用检测机制。该方案通过将数据存储在客户控制的云基础设施中,解决了企业在使用前沿模型时的安全合规困境,预计今秋分阶段向 Claude Code、Bedrock 等平台用户推送。
报道正文
本文目录7 个章节

今天,我们宣布推出企业前沿安全防护(Enterprise Frontier Safeguards, EFS)。这是一项将零数据保留(Zero Data Retention, ZDR)的隐私保护特性与最先进的滥用检测防护机制相结合的解决方案。EFS 的工作原理是将数据存储在由客户而非 Anthropic 控制的云基础设施中。EFS 将分阶段向客户推出,最早将于今年秋季晚些时候开始。为确保过渡平稳,符合条件的客户在 EFS 就绪之前,将在 Fable 5 和 Fable 5.1 上获得 ZDR 支持。
我们在开发 EFS 的过程中,与来自金融服务、医疗保健、制造业、电信、法律、零售及公共部门等行业的 100 多家客户,以及我们的云合作伙伴——亚马逊云服务(Amazon Web Services)、谷歌云(Google Cloud)和微软 Azure——进行了密切协作。
EFS 将支持以下平台:Claude Code、Claude Enterprise、Claude Platform、Amazon Bedrock、AWS 上的 Claude Platform、Google 的 Agent Platform 以及 Microsoft Foundry。
解决前沿安全困境
像 Claude Fable 5.1 这样的 Mythos 级模型,代表了智能水平和代理能力的大幅提升。然而,随着这种提升,也带来了滥用和自主行为失当的风险。
在过去几个月里,我们看到了大量试图滥用 AI 模型的证据。这些滥用行为范围广泛,从欺诈等典型滥用形式,到复杂的网络攻击,后者可能包括代理自主执行破坏性行为。其中一些案例涉及窃取或挪用企业客户的凭证,而在无法监控流量并检测异常行为的情况下,这类行为很难被发现。
此外,由于最复杂的滥用行为往往涉及跨越多个会话和账户的多项任务,仅对每次交互单独运行自动化分析并立即丢弃数据是不够的。有效的检测需要存储数据一段有意义的时间,以便能够跨时间和账户进行关联分析。
出于这个原因,我们从 Fable 5 开始引入了 30 天的数据保留政策。这一政策的初衷并非为了利用企业数据进行训练:Anthropic 从未在未获明确许可的情况下使用企业数据进行训练,未来也绝不会这样做。
与我们合作的企业通常理解数据保留在安全和防护方面的价值,但许多企业——尤其是受监管行业的企业——发现难以接受带有数据保留功能的模型。因此,我们与客户深入沟通,共同设计了一套解决方案,旨在兼顾两者的优势:既保留零数据保留(ZDR)的隐私保护特性,又具备跨时间和账户监控所带来的安全保障能力。
基于客户反馈的设计
我们在构建 Enterprise Frontier Safeguards(EFS)时,充分采纳了日常使用者的专家意见,包括安全、产品、合规和交付团队。我们合作的对象之一是系统性风险分析与韧性中心(ARC),其成员包括美国最大几家银行的首席信息安全官,如高盛、摩根士丹利、花旗集团、美国银行和富国银行。
我们还与康卡斯特(Comcast)、毕马威(KPMG)、万事达卡(Mastercard)、Salesforce 和 Visa 等公司的领导者合作,以确保该设计方案能够适应不同行业的需求。我们的对话覆盖了《财富》100 强中的四分之一企业、所有美国全球系统重要性银行,以及几乎所有受监管的行业。
以下是我们从这些广泛客户群体中收集到的反馈,以及我们在 EFS 中为解决这些普遍关切所采取的措施:
关于监控
企业长期以来一直通过监控来防范内部风险,现在他们希望提升针对智能体(agents)的监控水平。他们的担忧主要集中在 Anthropic 的自动化监控系统是否符合其监管标准。
借助 EFS,客户掌控数据审查方式。当监控检测到需要关注的模式时,相关信号会直接发送给客户,以便他们审查自动化系统检测到的内容。
关于数据存储
由于多种原因,企业增加另一个“可信数据供应商”是一项繁重的工作。他们需要通知所有客户这些供应商的身份并更新合同。此外,鉴于数据的高度敏感性,企业内部也有严格的安全存储和审计要求。基于这些顾虑,我们在架构 EFS 时确保客户能够将数据存储在其现有的云基础设施上。
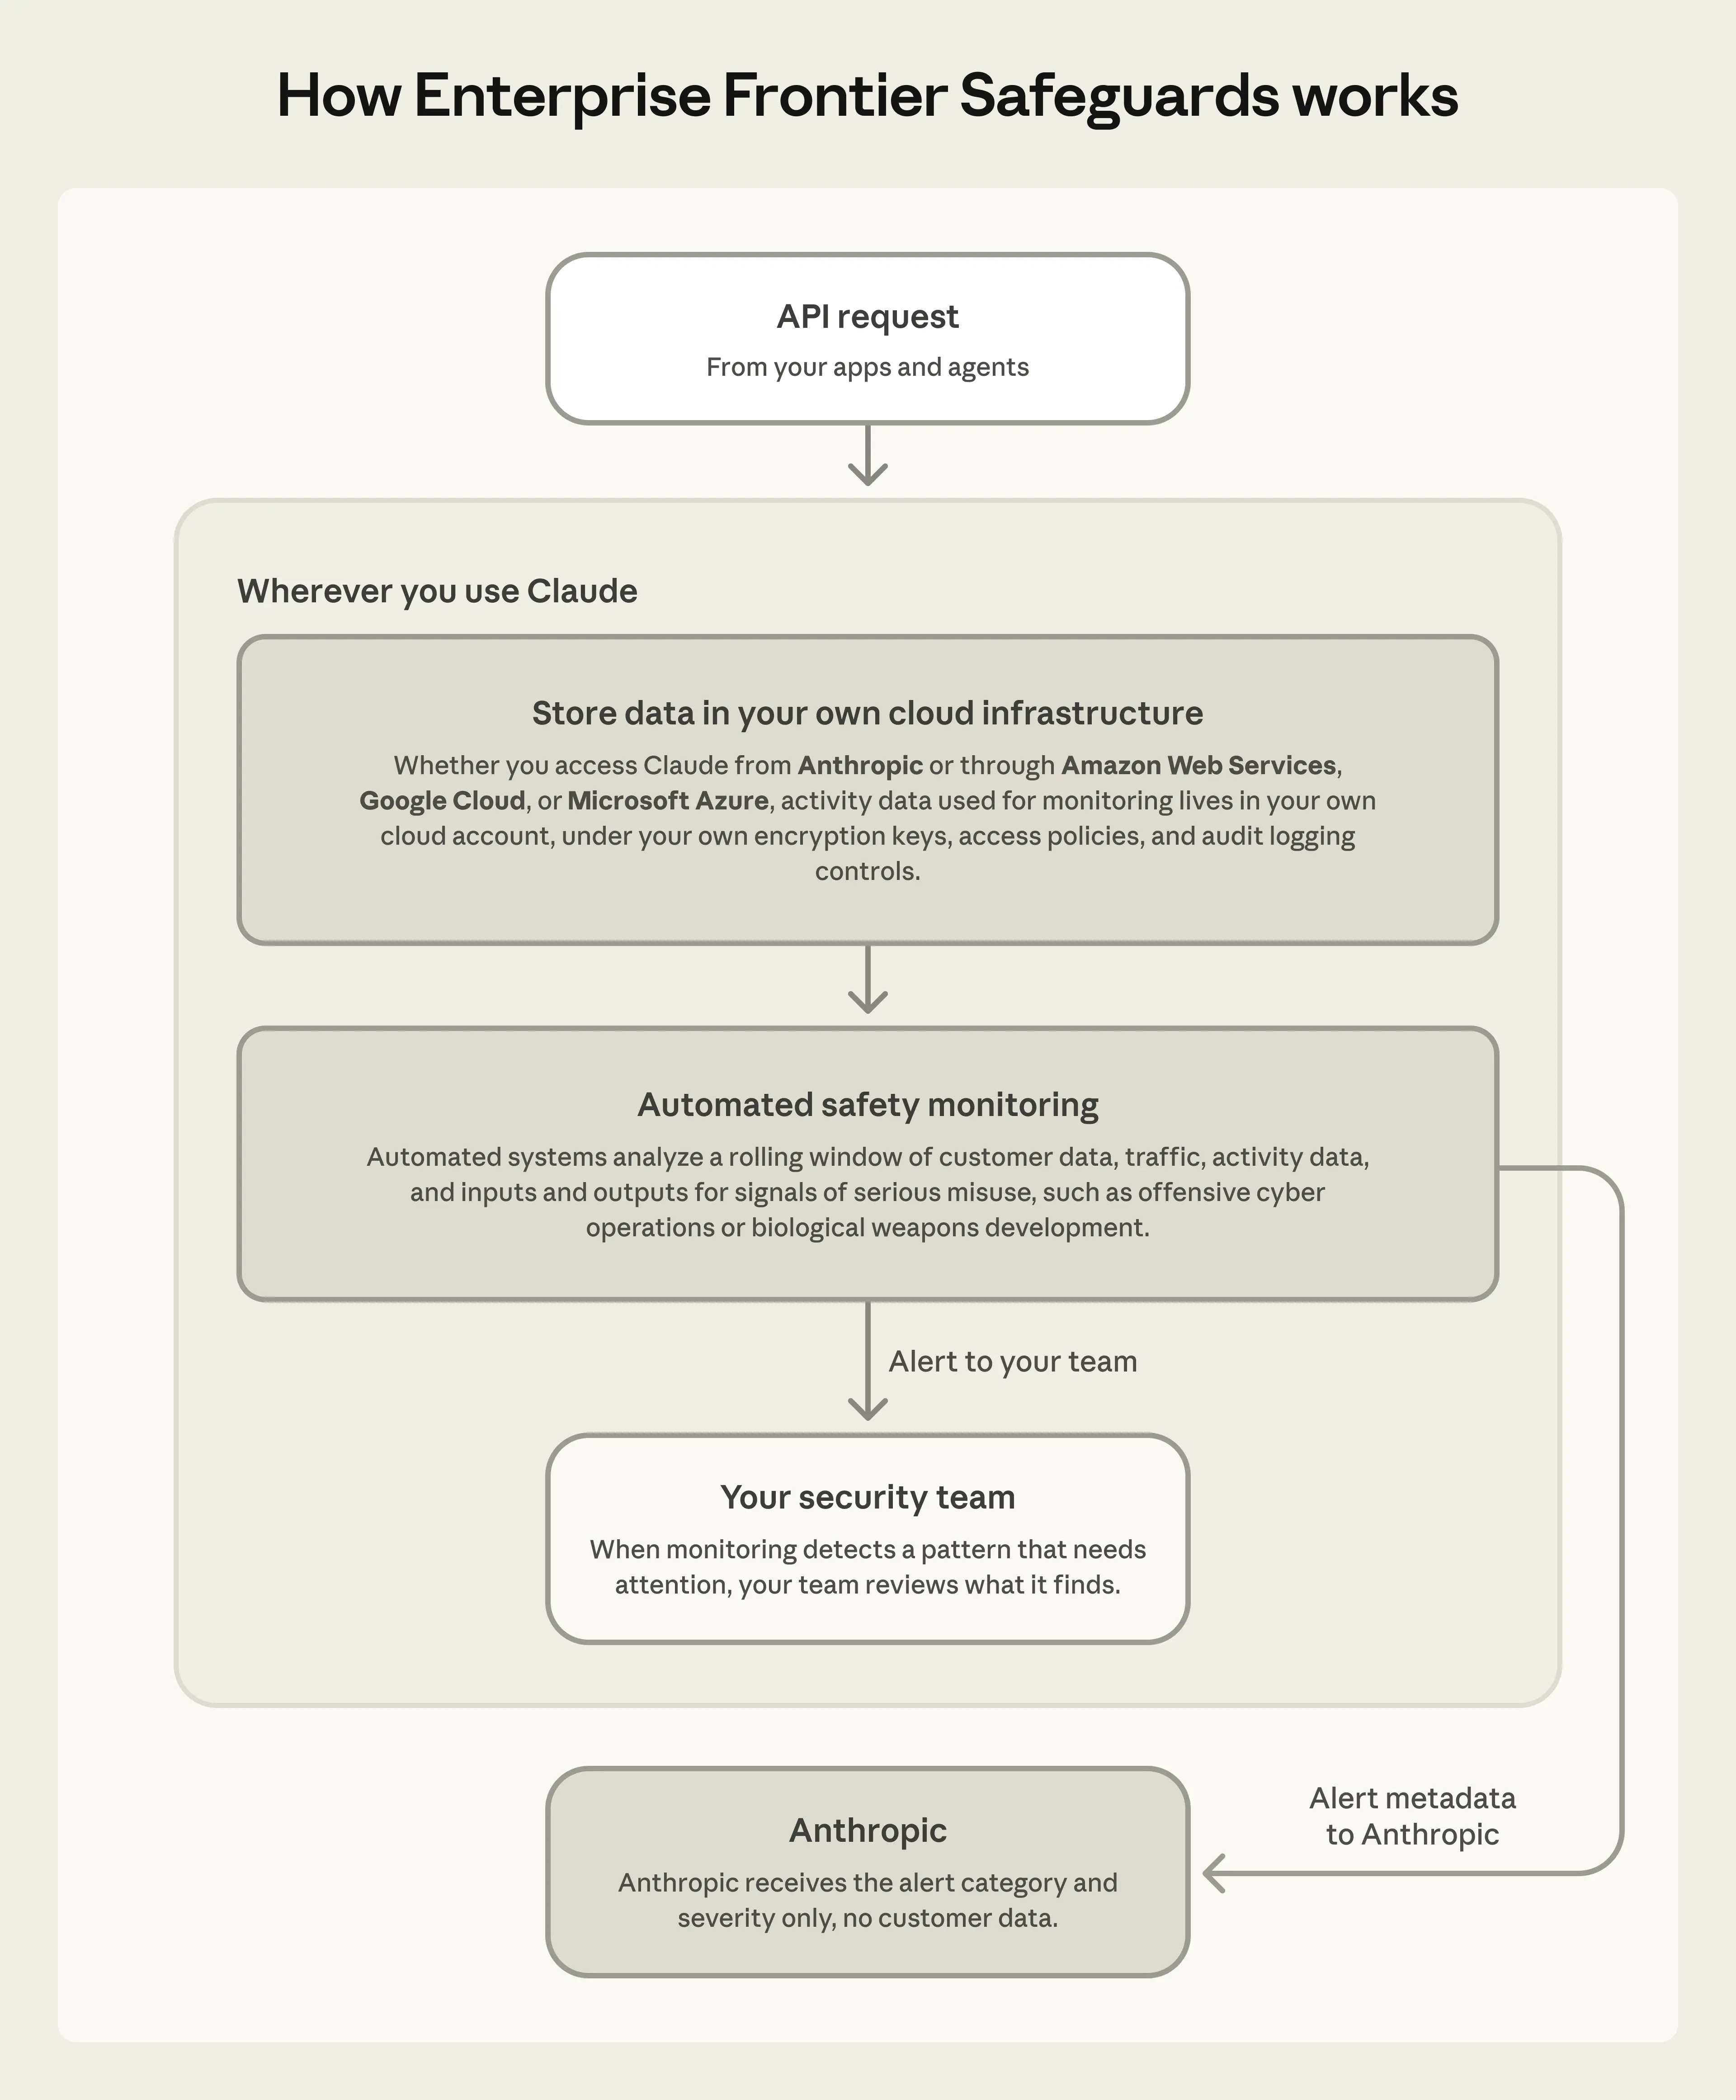
在 EFS 中,客户可以掌控其数据存储与管理。 客户希望数据能够驻留在他们自主控制的基础设施中,并受其自有的加密密钥、访问策略和审计日志保护。用于监控的活动数据可存储在客户自己的云账户中(例如 Amazon S3、Azure Blob Storage 或 Google Cloud Storage)。
关于自动化审查与人工审查
尽管自动化审查日益高效,但由人员复核标记内容仍具有价值,有助于确认真实滥用行为并排除误报。然而,我们从许多客户——尤其是受监管行业客户——那里听到的是,执行此类审查的人员必须是其内部员工。许多机构遵循严格规定,限制特定信息的可见范围,例如特权法律材料、非公开信息以及药物安全报告。他们的团队已经接受过相关培训并获得相应资质许可。
EFS 提供自动化安全监控,无需 Anthropic 进行人工审查。 客户希望防范网络攻击,并认识到如果攻击跨多个会话和账户展开,检测难度极大。通过 EFS,自动化系统会分析滚动时间窗口内的流量,以识别严重滥用信号,包括开发进攻性网络或生物能力的企图,以及凭证被盗或泄露的迹象。这些警报直接发送给客户,由其内部人员后续处理——无需 Anthropic 员工进行人工审查。
AI 控制措施的设计必须旨在保护敏感信息,而模型安全防护是该过程中的重要组成部分。Anthropic 在开发 Enterprise Frontier Safeguards 期间与我们合作,以确保符合我们的要求和标准。
Enterprise Frontier Safeguards 完全满足了我们提出的需求:我们的日志保留在 Wells 管理的环境中,并使用 Wells 管理的密钥。我们在 Anthropic 负责检测的同时,保持对数据的控制权。这种职责划分使我们的团队能够安全地应用前沿模型,并履行对客户、员工及监管机构的义务。我们参与塑造了这些安全防护措施,因为我们的行业亟需它们。
作为一家运营关键基础设施的公司,模型的能力至关重要。同样重要的是那些允许我们将数据保留在自己账户中的解决方案,Enterprise Frontier Safeguards 完美解决了这一问题。
我们的八位成员与 Anthropic 合作,明确了在系统重要性银行内部运行最强大的前沿模型所需具备的条件:数据由谁持有、密钥由谁掌控、自动化审查能看到什么以及不能看到什么,以及在何种条件下才允许人工介入查看。此次合作正推动更完善的安全保障措施和标准的开发与交付,这些措施和标准有望在我们的行业乃至更广泛的领域实现规模化应用。
安全保障架构的一个核心原则是,我们能够保留数据,并将其存储在模型本身之外,在我们的环境中受到保护。公司内以及客户工作的某些领域受到严格监管且高度敏感。正是这些安全保障措施,使我们能够将 AI 应用于此前无法涉足的业务环节。 服务合作伙伴
二十多年来,客户一直信任我们并委托我们管理其数据。正是基于这一经验,我们希望主动协助 Anthropic 深入探讨这一问题,而非袖手旁观。我们得以在架构层面(而不仅仅是政策层面)共同开发新的安全与隐私功能。
我们的客户希望将前沿模型投入实际应用,而其安全团队则要求数据保留在他们可控的基础设施中。Anthropic 已与上百家企业合作构建了“企业级前沿安全保障”(Enterprise Frontier Safeguards),旨在精准满足这一需求。 服务合作伙伴
随着 AI 模型承担更多受监管的敏感工作负载,负责任地扩展规模不仅取决于政策承诺,更取决于架构设计。对数据环境的直接控制权,结合基于模式的自动化安全监控,为企业提供了具体的结构性能力,使其能够在具备真正监督、问责机制和信心的情况下进行部署。 服务合作伙伴
关于安全保障措施及其设计——显然,你们听到了我们的反馈。他们让我们掌握了主导权。日志完全由我们控制;除非我们愿意,否则这些数据不会流向任何其他地方。这赋予了我们数据控制权、信息控制权,以及在检测到可能突破安全保障阈值的行为后,决定后续处理方式的权力。
随着 AI 在企业中的渗透日益加深,安全性和信任感是推动组织从实验阶段迈向大规模部署的关键因素。“企业级前沿安全保障”将从一开始就构建这些要素:监控数据保留在客户可控的基础设施中,并由客户自己的团队决定谁有权访问这些数据。 服务合作伙伴
[注:本文篇幅超长,以上为核心前篇精译,后续内容保留原文呈现]
Keeping customer data confidential is a promise Snowflake makes to every customer. We've always moved fast getting frontier models into their hands. The hard part was doing that safely under the strictest data guarantees. We partnered with Anthropic to design Enterprise Frontier Safeguards so we can do both: data stays in the customer's environment, under keys they control, running Anthropic's most capable models from day one. This is what responsible frontier AI looks like when it's built with platforms in mind.
At Stripe, protecting customer data is foundational to how we operate. Anthropic’s Enterprise Frontier Safeguards willenable us to use covered frontier models while retaining conversation logs in Stripe’s AWS environment, with access and review governed by Stripe’s security controls.
Rogo’s customers expect access to the best intelligence available, but never at the expense of security and guardrails around their data. Enterprise Frontier Safeguards will bring the most capable models to financial institutions while meeting the institutional-grade data requirements they demand. That combination of frontier intelligence and enterprise-grade controls is critical to deploying AI across financial services.
FIS powers the infrastructure behind how money moves and how financial institutions operate, so any AI safeguard we deploy has to meet that scale and standard of trust. Our partnership with Anthropic already includes testing their most advanced frontier models against our own systems through Project Glasswing. Claude Enterprise Frontier Safeguards expands that work, keeping retained data in our own account and routing flags directly to our security team.
Companies trust Cognition's autonomous engineers with real production work, and that trust depends on their work staying private. With Enterprise Frontier Safeguards, customer data and identities never leave our side. It will let us bring frontier AI to production work, no privacy tradeoff required.
Our customers' code and data are some of their most valuable intellectual property. Protecting that information is foundational to how we build at Factory. Together with Anthropic, we're enabling customers to use Claude's most capable models while keeping control of proprietary data in their hands. Enterprise Frontier Safeguards gives enterprises access to frontier intelligence with the data protections their security teams require.
We have always maintained an unwavering commitment to client confidentiality and security. The leading legal and professional teams we serve view these principles as nonnegotiable, and we hold ourselves to the same standard. Enterprise Frontier Safeguards reflects this commitment, enabling customers with the most rigorous confidentiality requirements access to frontier models without the model provider retaining their data.
01 / 17
How EFS works
These controls are designed to work the same way whether you access Claude directly from Anthropic or through a cloud partner. Customers on Amazon Web Services, Google Cloud, and Microsoft Azure will get equivalent controls, with their activity data stored in their own cloud account, in the environment they already trust. We’re also working to support third-party offerings that serve customers that are eligible for Enterprise Frontier Safeguards.
Customer-owned storage, Customer-Managed Encryption Keys, and fully automated review are each opt-in, so you enable the ones your organization needs. None of them change model behavior, API pricing, or rate limits.
Anthropic doesn’t charge for Enterprise Frontier Safeguards. If customers elect to store their data in their cloud account, their cloud provider bills them for that storage, as well as reads, writes, and data egress fees, the same way it bills any other resource.
Getting started
Enterprise Frontier Safeguards will roll out to customers in phases, with the goal of making it broadly available later this fall. To request access to Enterprise Frontier Safeguards, please complete this form.