Railway 遭入侵强制轮换密钥 AI 平台成攻击目标
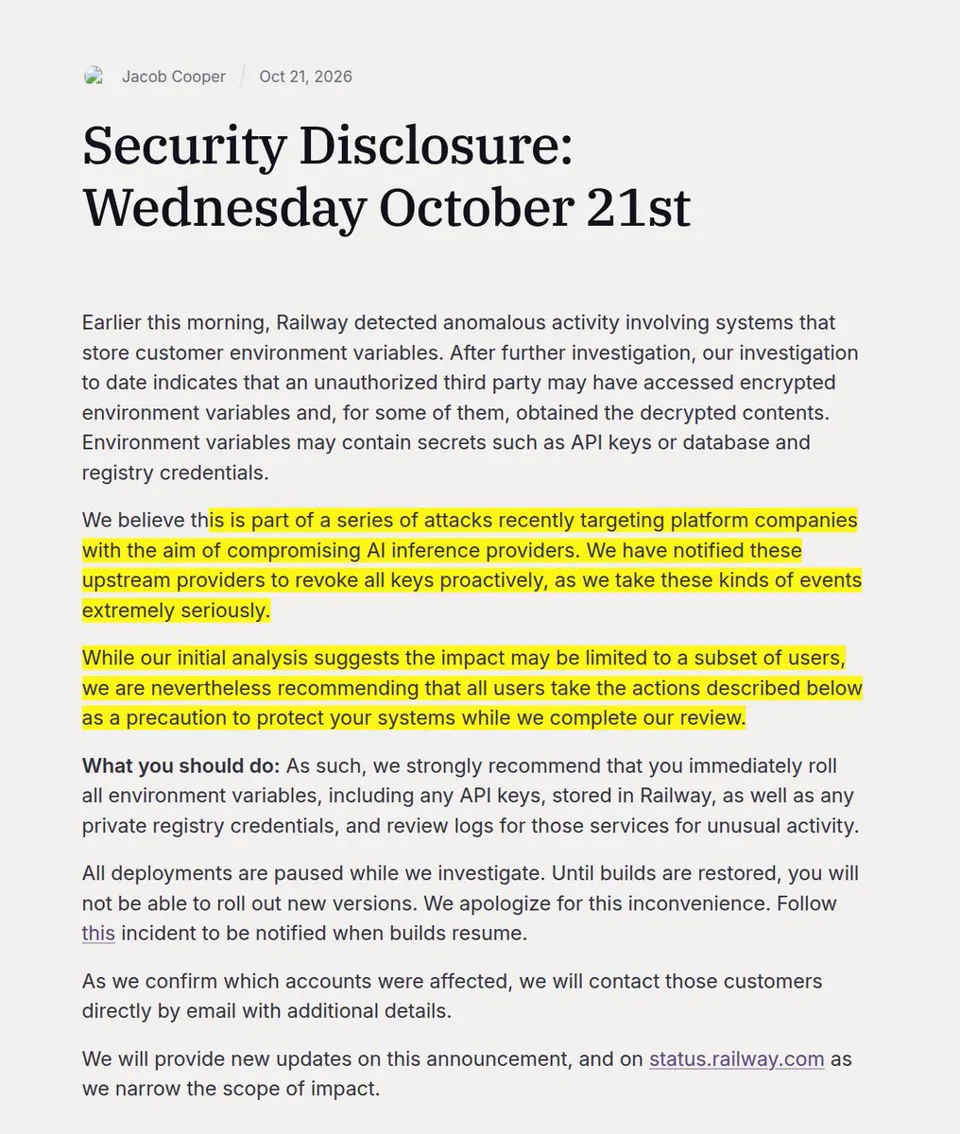
开发者平台 Railway 因入侵者解密存储凭证,要求所有客户立即轮换包括模型 API 密钥在内的机密信息。此次事件被关联至针对 AI 推理提供商的一系列攻击,旨在窃取前沿模型数据以训练竞品,此前 OpenCode 也报告了类似的安全漏洞。
报道正文
Rohan Paul (@rohanpaul_ai) · 2026-10-22 14
Developer platform Railway told every customer to rotate all secrets after an intruder decrypted some stored credentials.
Those environment variables hold database passwords, cloud keys and model API keys, letting anyone holding them sign in as the owner.
Railway said a subset of users may be affected, yet it froze all deployments and reset bucket keys and GitHub tokens itself.
It tied the intrusion to a string of attacks on platforms aimed at AI inference providers, and asked those providers to revoke keys.
Days earlier, OpenCode blamed a distillation attack for a breach possibly exposing OpenAI, Anthropic and Google keys saved by 1.4% of Console users.
Stolen keys let attackers harvest frontier-model answers for training rival models while victims pay the bills.